Martin Roesch: The Side Project That Became a $2.7 Billion Company
Martin Roesch is one of the open source community's most revered developers, best known for creating the Snort intrusion detection and prevention system.
His free software brought top-of-the-line cybersecurity to the masses, and his savvy business model inspired countless others to make a living off their software without compromising their open-source principles.
So what made Martin Roesch's approach to cybersecurity so revolutionary — and what can today's tech world learn from his story?
Martin Roesch at a Glance
- An astronomy nerd turned cybersecurity fanatic, Martin Roesch was an early member of the open-source software community that took off in the 1990s.
- In 1998, after noticing a lack of affordable, accessible intrusion detection and prevention systems (IDS/IPS), he decided to create his own: Snort.
- Snort was released as a free, open-source download, but its packet sniffing and threat response capabilities rivaled those of expensive commercial products.
- Roesch founded Sourcefire in 2001 and released a paid version of Snort, Sourcefire 3D System, with enhanced features and support targeted at commercial users.
- In 2013, Sourcefire was acquired by Cisco for $2.7 billion, and Roesch continued to lead its development until 2019.
- Today, Snort is considered one of the best IDS/IPS tools — and one of the best pieces of open-source software — ever created, with over 5 million downloads and 600,000 users.
The Life of Martin Roesch
Martin Roesch's Early Life
As one might expect from a cybersecurity expert, Martin "Marty" Roesch has kept much of his early and personal life private. But what he's revealed illustrates how an early passion can blossom into an iconic career.
Roesch grew up curious about science, especially astronomy and the emerging field of computer science. He spent his adolescence stargazing and learning how his telescope worked, from the robotics to the optics.
In 1988, Roesch enrolled at Clarkson University as an Electrical and Computer Engineering major. After graduating in 1993, he worked as a systems and network engineer at various companies, including Stanford Telecom and GTE Internetworking.
The Creation of Snort
As the new millennium approached in 1998, igniting a global frenzy of technological preparations for Y2K, Roesch was ramping up his cybersecurity in a more subtle way.
During the day, he worked a job reviewing contracts at the U.S. Department of Defense. In his free time, he researched cybersecurity and began brainstorming ways for the world to protect itself against increasingly powerful — and increasingly common — cyberattacks.
At the time, antivirus software was able to scan downloads and existing files for malware, and firewalls could prevent outside hackers from infiltrating networks in certain predefined ways. But when it came to stealthy intrusions, previously unseen tactics and attacks originating from within a given network, security software fell short.

- Five gigabit ports with up to three WANs, an SPI firewall, DoS defense and IP/MAC/URL filtering, plus IPsec, OpenVPN and L2TP tunnels. Home-lab security on a budget.
Such advanced cybersecurity — real-time, automated intruder detection that could identify anomalous traffic and assist in analyzing it — was largely the domain of militaries, governments and academic research. And the programs that were available to the public were prohibitively expensive for all but the most wealthy users.
Thus, private organizations and individuals were, for the most part, left to fend for themselves against the ever-changing landscape of cyberattacks.
But Roesch saw both sides of the situation.
At the Department of Defense, he was tangential to some of the latest and greatest cybersecurity developments. But at home, he spent a lot of time in the burgeoning open-source software community, where talented programmers collaborated on projects that anyone could download and use for free.
He decided to bridge the gap by creating a free, open-source intrusion detection and prevention system (IDS/IPS) for Linux, the preferred OS of most cybersecurity geeks. The program he envisioned would be highly customizable and adaptable, yet still accessible enough that anyone could use it to monitor their network for suspicious activity of all types.
From Snort to Sourcefire
To Roesch, a tool that could allow the user to "sniff" (read) network packets, scan and analyze network traffic in real time, and automatically respond to intrusions based on user-defined rules seemed like a must-have for any security-savvy computer user.
But when he released the first version of his creation, Snort, in November 1998, he was surprised at just how many people felt the same way.
The open-source community took to Snort instantly, with many members volunteering their time and expertise to the project. Snort quickly racked up thousands of downloads and became more robust as Roesch and the other contributors began building more comprehensive rule sets.

- A passive gigabit Ethernet tap that mirrors traffic to Snort, Wireshark or any sniffer without dropping a packet, powered from a USB port. The clean way to monitor a link.
By 2001, Snort had been downloaded over four million times, making it the most popular IDS/IPS in history. At tech conferences, people recognized Roesch and clamored for a chance to speak to him about Snort — he'd become as close to a household name as a cybersecurity expert could get.
But his current way of life was unsustainable. Roesch had been maintaining Snort in his free time while working a day job as a software engineer at a startup, but was now finding that Snort demanded more attention than he could spare.
Not wanting to abandon his pet project but still needing to earn a living, Roesch devised a way to monetize Snort without compromising its free, open-source ethos. He'd create a beefed-up enterprise version of Snort and charge organizations to use it, allowing him to continue offering it for personal use at no charge.
Roesch left his job and founded a startup of his own: Sourcefire. The new commercial version of Snort was called Sourcefire 3D System, which combined a hardware security appliance with Snort's IDS/IPS capabilities and a centralized management console.
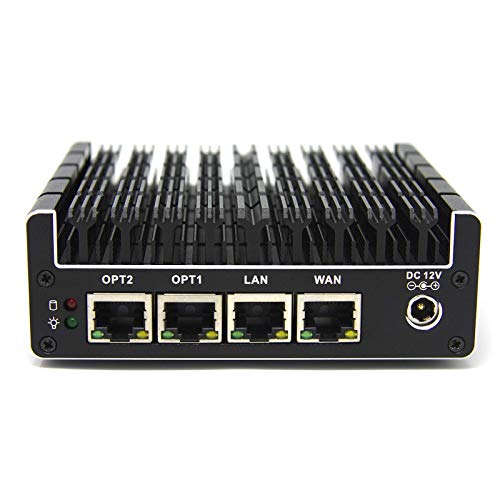
- Quad-core Intel with AES-NI, four Intel gigabit ports, 4GB RAM and a 32GB SSD, silent and ready for the open-source firewall of your choice. No OS preinstalled, US-based support.
Starting Sourcefire was a risky move for Roesch, as he was now responsible not just for himself and his software but also his four new employees — and the reputation of an entire company. But Roesch had always been a risk-taker, and this one paid off: Sourcefire raised $56.5 million in initial financing.
Sourcefire Changes Hands
Backed by substantial funding, Snort and Sourcefire grew to rival even the most established, advanced commercial IDS/IPS products — and other cybersecurity companies were scrambling to cope.
In 2005, one such company approached Roesch and Sourcefire with a tempting offer. Check Point Software, which produced similar network security products to Sourcefire, wanted to acquire the company.
Combining the Check Point and Sourcefire customer bases and technologies, Roesch thought, would create a cybersecurity powerhouse with the resources to stay on the cutting edge of IDS/IPS software. The two companies came to an agreement: Check Point would buy Sourcefire for $225 million.
But the U.S. government wasn't so keen on the idea. Sourcefire's products were used by various U.S. military and government agencies, but Check Point was an Israeli company, and the prospect of a foreign entity controlling a software product used by the government sparked national security concerns.
The Committee on Foreign Investment in the United States, which governed such international acquisitions, made it clear that it intended to block the Sourcefire purchase. Check Point relented and backed out of the deal, declaring that it'd still partner with Sourcefire in a more limited, independent capacity.
Two years later, in 2007, Sourcefire went public, raising $86.3 million in its IPO. The following year, Barracuda Networks, a network security company, offered to buy Sourcefire for $187 million, an offer that Sourcefire rejected.
Switching to Cisco
By 2009, Sourcefire 3D System had become the IDS/IPS of choice for 80% of Fortune 100 companies and 42% of Global 500 companies. And its growth wasn't slowing: each new quarter saw revenue increases of around 30%, and at the end of 2012, it held $204 million in cash and investments.
Acclaim wasn't limited to the financial sphere, either. Snort was named the best IDS/IPS by SC Magazine, and Sourcefire 3D System was awarded top marks by Network World, NSS Labs, ICSA Labs and the Gartner Magic Quadrant competition.
These accolades drew the attention of a true tech behemoth: Cisco Systems.
Cisco was looking to enhance its IPS offerings, which Sourcefire had already mastered. Sourcefire also had a substantial portfolio of government and enterprise customers, a roster of skilled cybersecurity experts and engineers, and a stellar reputation across nearly every industry.
In 2013, Cisco announced that it was acquiring Sourcefire for $2.7 billion. This time, the government didn't block the acquisition, and Roesch found himself leading not just the Sourcefire team but also Cisco's Security Business Group division.
The Sourcefire 3D System product line was renamed Firepower, and development expanded into cloud security and other nascent fields.
- Hardware-accelerated WireGuard and OpenVPN, three 2.5G ports with multi-WAN failover, VPN obfuscation and deep packet inspection, all on OpenWrt. No Wi-Fi, by design.
But while Roesch continued working on Firepower as well as Snort, his entrepreneurial spirit didn't mesh with the new corporate bureaucracy he found himself in. In 2019, he parted ways with Cisco and Firepower to focus more on Snort — and explore new ventures.
Martin Roesch Today
Since 2016, Roesch has served on the board of Threat Quotient, a threat intelligence, analysis and sharing company. He also worked as a founder advisor at Decibel Partners, a venture capital firm focused on IT and partnered with Cisco, from 2019 to 2022.
In 2021, he founded Netography, which produces a cloud threat detection platform based on machine learning and advanced analytics. It incorporates Snort's packet sniffing and network traffic analysis functions, representing the next evolution of IDS/IPS.
And 24 years after he wrote its first lines of code, Roesch is still working on Snort, which continues to be free and open-source. It now boasts over 600,000 registered users and 5 million downloads, and it's been repeatedly named one of the greatest pieces of open-source software of all time.
Martin Roesch: Nothing to Snort At
At the end of the 1990s, Martin Roesch's life centered around cybersecurity: a day job at a startup and a spare-time project aimed at bringing better security to the masses.
He's since shown that he can build a business as well as a security tool, developing a commercial model for open-source software and negotiating a $2.7 billion sale to Cisco.
Through it all, Snort and the free, open-source movement have stayed at the center of his career. The business grew around the tool, and the tool remained available to everyone.
What Is the Purpose of an IDS?
What Is Packet Sniffing?
QUOTE:
"Amateurs hack systems, professionals hack people."