Mikko Hyppönen: The Virus Hunter Who Beat Three Worms in Two Weeks
Long considered one of the best minds in technology, Mikko Hyppönen has been waging war on malware for over 30 years.
Born in Finland in 1969, he's since been on the front lines of some of the biggest cybersecurity attacks in history. And when he's not fighting malware, he's spreading his vast knowledge of digital security and privacy around the world.
Mikko Hyppönen at a Glance
- Mikko Hyppönen made his name as a cybersecurity researcher for F-Secure.
- In 2003, he and his team took down three of history's worst viruses in just a couple of weeks: Blaster, Welchia and SoBig.F.
- Hyppönen's reverse engineering skills and quick thinking made him an in-demand cybercrime consultant for governments and militaries around the world.
- In 2011, Hyppönen analyzed the infamous Stuxnet worm that plagued Iran's nuclear facilities, concluding that it was most likely created by the US government.
- That year, he also traveled to Pakistan to interview the creator of Brain, the first PC virus.
- In response to the IoT malware epidemic, Hyppönen created Hyppönen's Law in 2016, which states that "if it's smart, it's vulnerable."
The Life of Mikko Hyppönen
Mikko Hyppönen entered the world of cybersecurity in 1991, when the internet was just beginning to play a role in the lives of everyday people.
Back then, he was a security researcher at F-Secure (then called Data Fellows), a Finnish company known for developing the world's first heuristic antivirus software. He developed the company's research lab, becoming its chief research officer in 1999.
Hyppönen in 2003: The Year of the Virus
Hyppönen rose to international fame in August of 2003, when he and his team at F-Secure identified and took down numerous pieces of sophisticated, widespread malware.
That year, Hyppönen says, was the worst year in virus history, and August was its worst month.
The Blaster Worm
The chaos began on August 11 with the Blaster worm, which exploited a security hole in Windows XP and could spread automatically to any vulnerable computer with an internet connection. Blaster hijacked its victims to conduct a DDoS attack against the Windows Update website, consuming system resources so heavily that many infected computers began rebooting uncontrollably.
Within hours of Blaster's release, Hyppönen's team had identified it. They coordinated with other antivirus companies to warn users about the worm and urge them to download Microsoft's official security patch.
The Welchia Worm
The following week, a new worm emerged: Welchia, a "helpful worm" designed to spread itself to as many computers as possible, remove the Blaster worm and install security patches to prevent reinfection.
But Welchia was coded in such a way that it clogged up networks, caused random reboots and interfered with enterprise IT functions. Many rail systems on the US's east coast were disrupted, as were Air Canada's check-in system and countless personal computers.
Hyppönen and his team worked quickly to create a tool to stop the Welchia worm, then put it online as a free download.
But as soon as that problem was dealt with, another appeared — and this one was the worst of them all.
The SoBig.F Worm
In January of 2003, Hyppönen identified a new email worm. It spread via infected email attachment, laid in wait for a short time, then surreptitiously downloaded more malicious files: keyloggers, backdoors and spam servers.
Hyppönen called it the SoBig worm and quelled its spread quickly by instructing email providers to block all emails from the SoBig email address. But new variants of the worm continued to pop up throughout the year, each one more sophisticated than the last.
On August 19, after a long week dealing with Blaster and Welchia, one of Hyppönen's researchers spotted yet another SoBig variant for the first time.
The team named it SoBig.F, and Hyppönen saw right away that it was leagues apart from its predecessors. It could spread so quickly as to seem unstoppable, and it was scheduled to download an unidentified program in three days' time.
Within a few hours, Hyppönen had written and released a program to detect and remove SoBig.F from infected computers. But there were still hundred of thousands of vulnerable users, each sending and receiving thousands of spam emails — and imminently set to experience an even worse infection.

- Multi-layer malware and ransomware defense, webcam and microphone monitoring, anti-phishing and a hardened banking browser for Windows, Mac, iOS and Android. The code ships on a card.
Hyppönen and his team spent the next several days reverse engineering the worm, eventually identifying its 20 originating servers around the world. They then tried to get ISPs and governments to shut those servers down before they could begin serving the malicious download.
Ultimately, 19 of the 20 servers were shut down, and the remaining server was so bogged down with traffic that it never executed its payload. Hyppönen, having saved millions of computers from an unknown fate, was hailed as a cybersecurity hero.
Hyppönen Goes Global
Throughout the 2000s and 2010s, Hyppönen continued his work with F-Secure. But he also saw his newfound fame as an opportunity to educate the populace about cybersecurity.
Hyppönen began traveling around the world, giving presentations to militaries, industry groups, students and the general public. These ranged from highly technical keynotes at hacker conventions to lectures at Stanford University to TED talks.
Additionally, Hyppönen began offering personal advice to governments facing cybersecurity threats in the US, Europe and Asia.
In 2007, he was named one of PC World's 50 Most Important People on the Web. That same year, he joined the advisory board of the International Multilateral Partnership Against Cyber Threats (IMPACT), a UN-backed cybersecurity alliance.
By 2011, Hyppönen was writing columns and articles for the New York Times, CNN, Scientific American and other world-renowned publications. Several of them addressed the then-unknown origins of Stuxnet, the ultra-sophisticated malware that attacked Iran's nuclear plants, with Hyppönen correctly surmising that it was created by the US government.

- Alex Gibney's 2016 documentary thriller on the Stuxnet cyberattack launched by the U.S. and Israel, and the malware that escaped its target. Required viewing for anyone who reads about cyberwar.
His profile grew even higher that year when he debuted his documentary, "Brain: Searching for the First PC Virus in Pakistan" to global acclaim. The film chronicled his trip to Pakistan to meet and interview the creator of Brain, widely considered the world's first computer virus.
Hyppönen's Law
As the Internet of Things expanded rapidly in the 2010s, Hyppönen recognized it as a cybersecurity nightmare. Smart lightbulbs, appliances, sensors, accessories and other gadgets were generally poorly secured, causing a huge spike in IoT malware attacks.
This prompted Hyppönen to issue a cautionary tweet in 2016: "Hyppönen's Law: Whenever an appliance is described as being 'smart', it's vulnerable."
His clear, succinct message — and the seriousness of its implications — brought Hyppönen's name to the headlines once again. The Law took hold so strongly that it formed the basis of Hyppönen's 2021 book, "If It's Smart, It's Vulnerable."
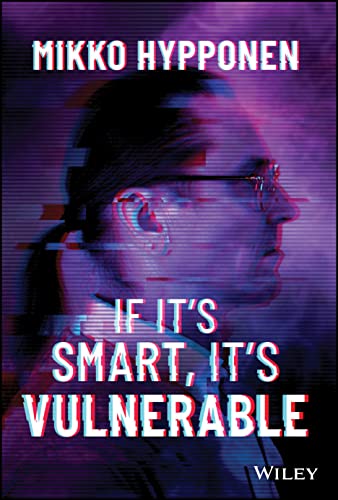
- Hypponen turns thirty years of virus hunting into a readable tour of malware, privacy and the Internet of Things, built on the law that bears his name. For readers who want the whole picture.
Mikko Hyppönen: Champion of Cybersecurity
Today, millions of virus researchers around the world owe much of their knowledge to Mikko Hyppönen.
For over 30 years, he's worked to explain how malware behaves and how people can protect themselves and their data.
Whether he's investigating a new worm, revisiting an infamous old one or explaining Hyppönen's Law, he makes the risks easier to understand — and harder to ignore.
F-Secure: An In-Depth Look at the Finnish Cybersecurity Powerhouse
Are Your IoT Devices Spying on You?
QUOTE:
"Amateurs hack systems, professionals hack people."