Nataly Vovk
- The Second Disruption of ALPHV/BlackCat Operations
- APT29’s Cyber Espionage Evolution: Adapting to Cloud Security Challenges
- Major Brands’ Subdomains Compromised to Send Millions of Malicious Emails
- Top Cyber Defense Strategies for U.S. Water Systems
- Knight Ransomware Source Code Available for Sale
- Operation Cronos: International Force Disrupts LockBit Ransomware Network
- U.S. Offers a Multi-Million Dollar Reward for Information about ALPHV/Blackcat
- Microsoft Warns about Russian State-Sponsored Espionage Attacks
- Medusa’s Strategic Evolution: Blending Extortion and Stealth in Ransomware Operations
- Threat Actors Posing as Ethical Hackers
The Second Disruption of ALPHV/BlackCat Operations
The ALPHV/BlackCat infrastructure experienced its second shutdown since December 2023. Key Takeaways The affiliate alleged that the operator pocketed a $22 million ransom payment for […]
The Second Disruption of ALPHV/BlackCat Operations Read More »
APT29’s Cyber Espionage Evolution: Adapting to Cloud Security Challenges
APT29, associated with the Russian Foreign Intelligence Service (SVR), is shifting its focus to launch attacks on the cloud services of its targets. Key Takeaways
APT29’s Cyber Espionage Evolution: Adapting to Cloud Security Challenges Read More »
Major Brands’ Subdomains Compromised to Send Millions of Malicious Emails
SubdoMailing phishing campaigns exploit the trust in major brands by hijacking their subdomains to flood inboxes with malicious emails. Key Takeaways Over 8,000 domains and
Major Brands’ Subdomains Compromised to Send Millions of Malicious Emails Read More »
Top Cyber Defense Strategies for U.S. Water Systems
U.S. government agencies released a defensive strategy that water utilities should adopt to enhance the protection of their networks from cyberattacks. Key Takeaways The Cybersecurity
Top Cyber Defense Strategies for U.S. Water Systems Read More »
Knight Ransomware Source Code Available for Sale
The representative of the Knight ransomware is currently marketing the source code for its third version exclusively to one purchaser on a hacker forum. Key
Knight Ransomware Source Code Available for Sale Read More »
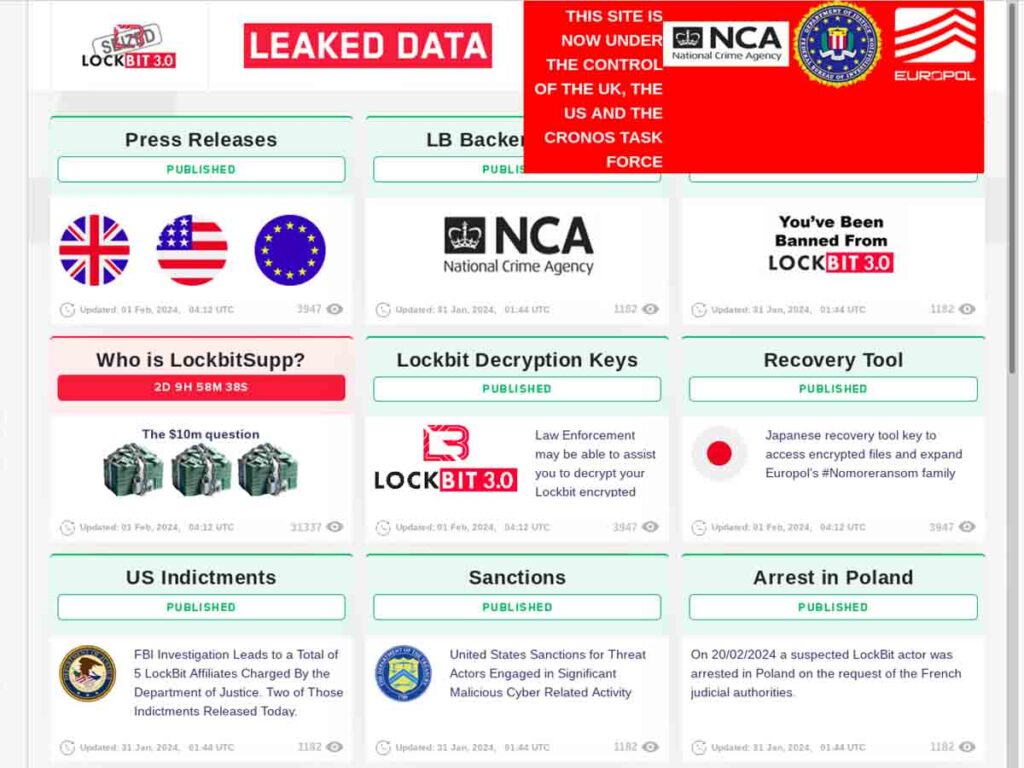
Operation Cronos: International Force Disrupts LockBit Ransomware Network
Today, the Department of Justice, alongside the United Kingdom and other global law enforcement bodies, announced a major operation against the LockBit ransomware group. Key
Operation Cronos: International Force Disrupts LockBit Ransomware Network Read More »
U.S. Offers a Multi-Million Dollar Reward for Information about ALPHV/Blackcat
The U.S. Department of State offered a reward for information leading to the ALPHV/Blackcat ransomware group. Key Takeaways On February 15, 2024, the U.S. Department
U.S. Offers a Multi-Million Dollar Reward for Information about ALPHV/Blackcat Read More »
Microsoft Warns about Russian State-Sponsored Espionage Attacks
On January 25th, 2024, Microsoft disclosed that the APT29 threat group, Russian state-sponsored hackers, were implicated in the November 2023 cyber attack on its systems.
Microsoft Warns about Russian State-Sponsored Espionage Attacks Read More »
Medusa’s Strategic Evolution: Blending Extortion and Stealth in Ransomware Operations
The Medusa ransomware group, active since late 2022, has intensified its activities in 2023, particularly after launching a data leak site on the dark web
Medusa’s Strategic Evolution: Blending Extortion and Stealth in Ransomware Operations Read More »
Threat Actors Posing as Ethical Hackers
A concerning trend has emerged in the digital security landscape in recent months. Victims of the notorious Royal and Akira ransomware attacks, which have caused
Threat Actors Posing as Ethical Hackers Read More »
QUOTE:
"Amateurs hack systems, professionals hack people."